Frequently Asked Questions
Frequently Asked Questions & Resources
Straightforward, plain-English answers about our retainers, audit timelines, testing models, and advisory scope.
An ongoing engagement where an Arann Tech team provides the strategic security leadership, risk management and compliance oversight a full-time security executive would, at a fraction of the cost.
Managed security providers monitor and respond to alerts. We focus on governance, risk, policy and compliance: the decisions and documentation that sit above the tools.
A named senior lead owns your account, supported by our team. You're never handed to a rotating pool of strangers.
We scope penetration tests, recommend independent testers from our partner network and help you act on the results.
It depends on your starting point. Most organizations need [X to Y] months (typically 8 to 16 weeks). A gap assessment gives you a realistic timeline.
Yes. We work remotely with clients across Canada and the US.
No advisor honestly can. We prepare you thoroughly, close gaps and help you present strong evidence.
Practical guides written for executives, boards, and engineering leadership.
A practical breakdown of testing exceptions, Complementary User Entity Controls (CUECs), and what to evaluate before signing contracts.
Request Guide →
How to evaluate organizational maturity, regulatory exposure, and budget when structuring security oversight.
Request Guide →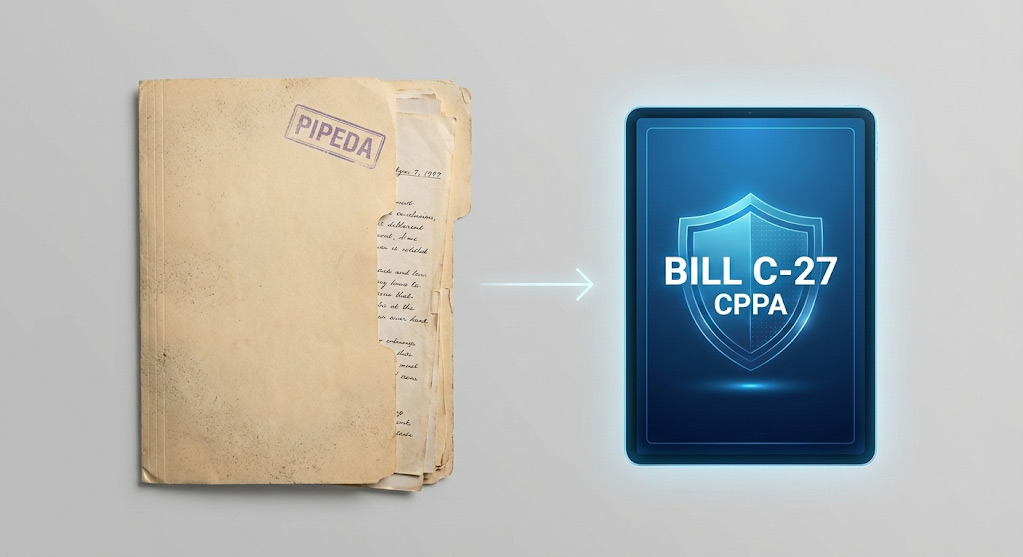
Demystifying Canadian federal statutory privacy requirements and mandatory breach reporting protocols.
Request Guide →
How to verify that third-party vendors aren't using your company's data to train external public models.
Explore Practice →
Accelerating enterprise sales cycles without agreeing to untenable liability clauses or audit overreach.
Request Guide →
Turning Spoofing, Tampering, Repudiation, Information Disclosure, DoS, and Elevation of Privilege into executive decisions.
Learn More →Book a free 30-minute call. We'll review your obligations and top risks and tell you plainly what you need and what you don't.
Speak with an Advisor