About Arann Tech
Translating technical risk into business resilience.
Arann Tech is a boutique cybersecurity advisory firm built on one idea: business leaders deserve clear security advice, not jargon.
We bridge deep technical risk expertise and executive decision-making. We don't sell unnecessary tools or rely on fear.
We provide the governance, risk and compliance frameworks that help your organization grow securely and earn the trust of enterprise clients.
Guiding rules behind every policy we draft, audit we run, and risk decision we support.
If we can't explain it simply, we haven't understood it.
Controls should match your actual risk, size and budget.
No product resale, no referral fees, no conflicts.
Decisions are documented and defensible.
Your program is backed by a team, not a single point of failure.
Arann Tech brings together senior security, risk and compliance practitioners from regulated and public-sector environments.
12+ Years in Technology • Governance, Risk & Compliance Leadership
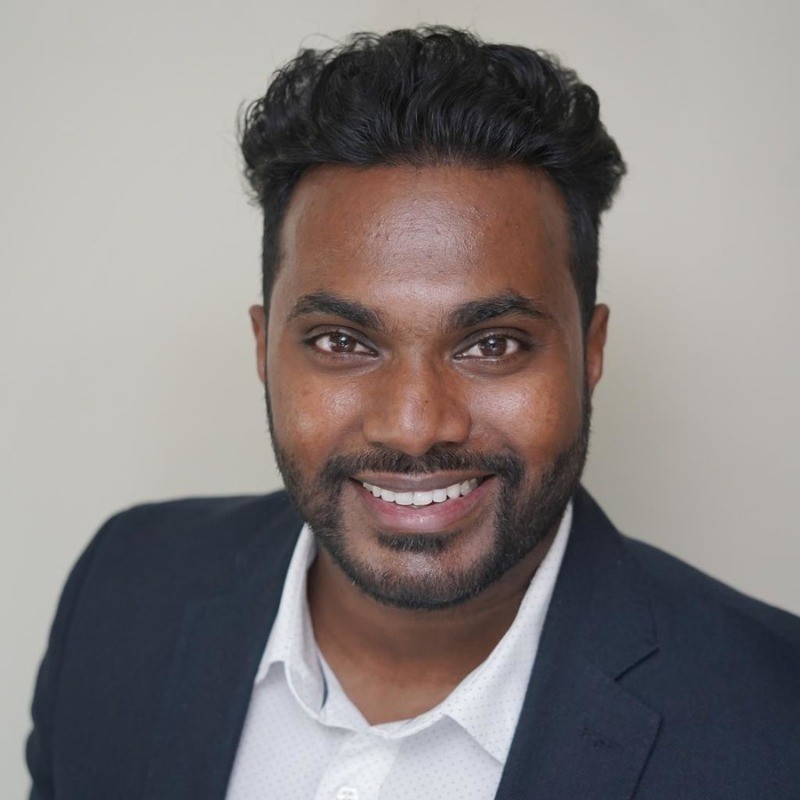
Jeneeit founded Arann Tech and leads its advisory practice. With more than 12 years in technology and a focus on governance, risk and compliance, he has designed identity and access management controls, led incident response operations, and managed enterprise risk registers in highly regulated environments.
His background in public-sector technical communications with the Legislative Assembly of Ontario shapes the firm's approach: turning dense statutory requirements and complex threat models into plain-language plans.
For penetration testing, forensics, legal and other specialties, we work with vetted independent partners, so you get the right expert without paying for a bloated bench.
"Your security program shouldn't be a black box. It should help your business move forward."
If you're an experienced GRC, risk or security consultant who values plain-English advice, we'd like to hear from you.