AI Governance & Security
Innovate with confidence. Manage the risk.
Adopt generative AI safely. AI risk assessments, acceptable use policies and vendor AI reviews aligned with ISO 42001 and the NIST AI RMF.
Your staff are probably already using generative AI, approved or not. Without clear rules, sensitive data can end up in public tools, and vendors may be using your information in ways you haven't agreed to.
Our AI governance practice helps you set practical guardrails so you can benefit from AI without creating privacy, legal or intellectual property exposure.
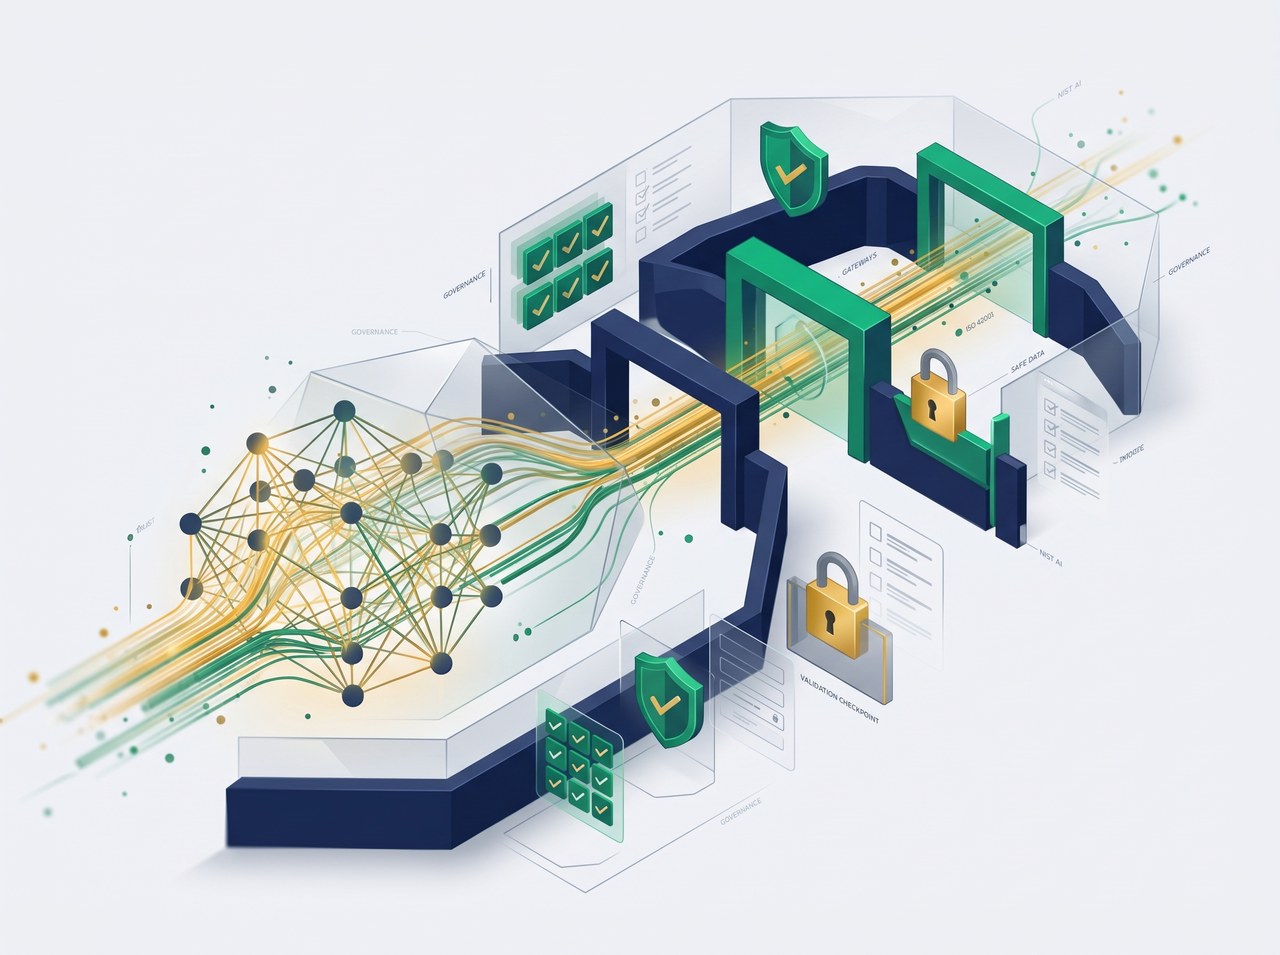
Everything required to govern generative AI safely across your organization.
We assess proposed AI integrations and SaaS tools against AI-specific risks such as prompt injection, data poisoning, sensitive data leakage and model denial of service.
We align your AI initiatives with ISO 42001 and the NIST AI Risk Management Framework, scaled to your size.
Clear, enforceable rules for employees on public and company-approved AI tools.
We evaluate how your software vendors use AI, what happens to your data, and whether it trains external models.
A catalogue of AI use across your organization with risk ratings and owners.
If employees have internet access, they are likely using it. A policy sets expectations and gives you something to point to.
Not for most organizations. Many use it as a framework for good practice, and some clients may begin to ask for it. We'll tell you what's proportionate for you.
A practical checklist to review how your organization uses AI today.
Delivered straight to your work inbox.