Cybersecurity Advisory & GRC Services
Security by design. Compliance by default.
Security leadership retainers, risk assessments, threat modeling and third-party risk management for regulated organizations in Canada and the US.
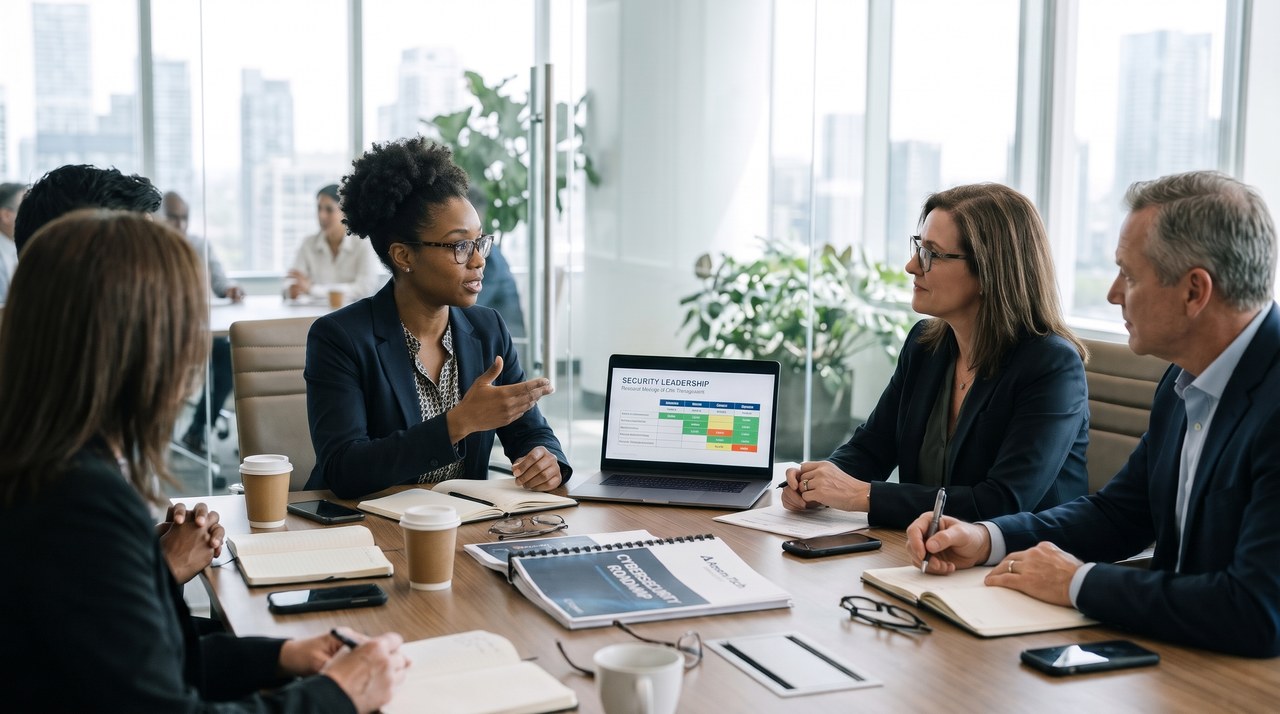
Security works best as an ongoing function, not a one-off project. Our retainers place a dedicated Arann Tech team behind your security program, with executive-level leadership at a fraction of the cost of building a security department.
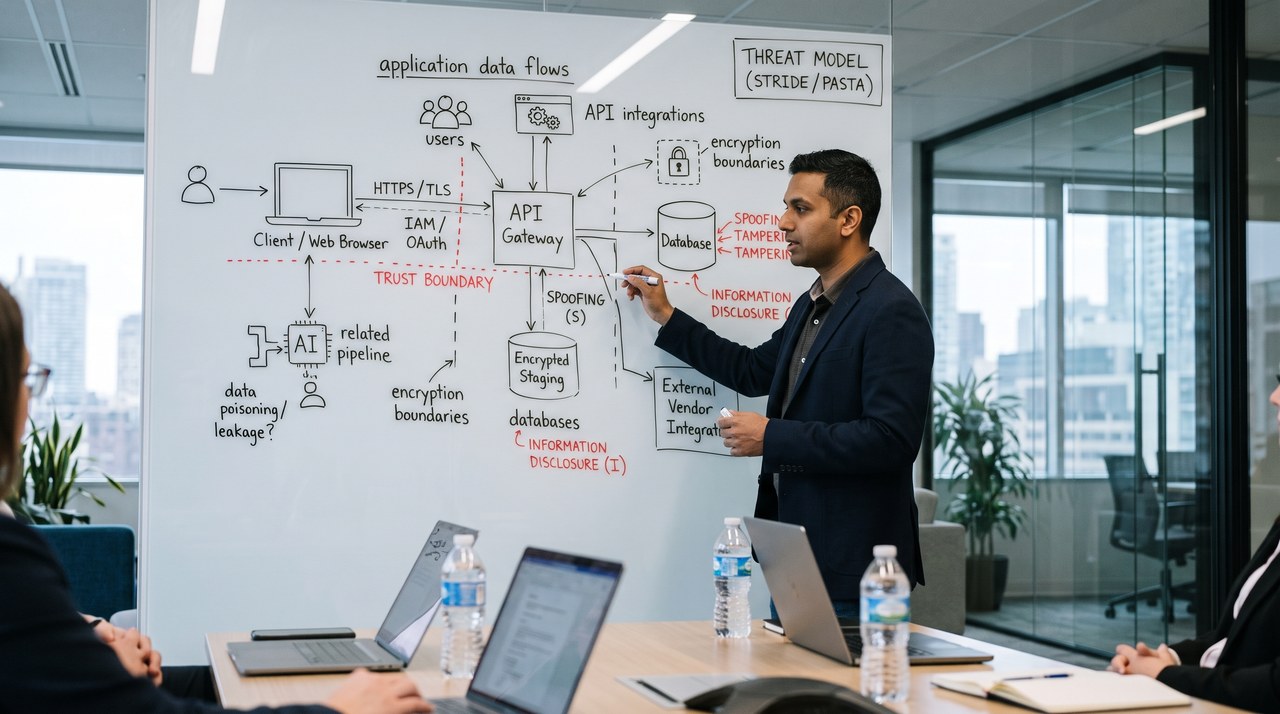
Before you launch a new application or migrate infrastructure, we examine how it's designed, not just whether a scanner finds known vulnerabilities.
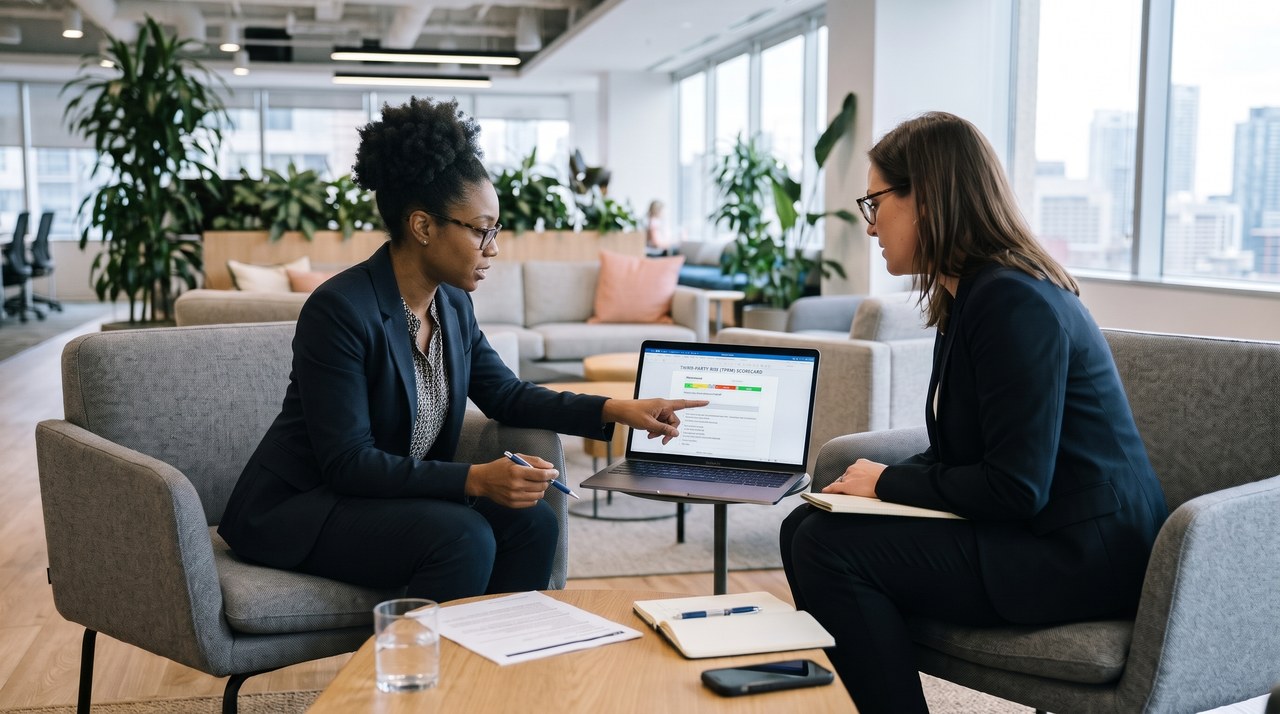
Your risk includes your vendors' risk. We take vendor due diligence off your team's plate.
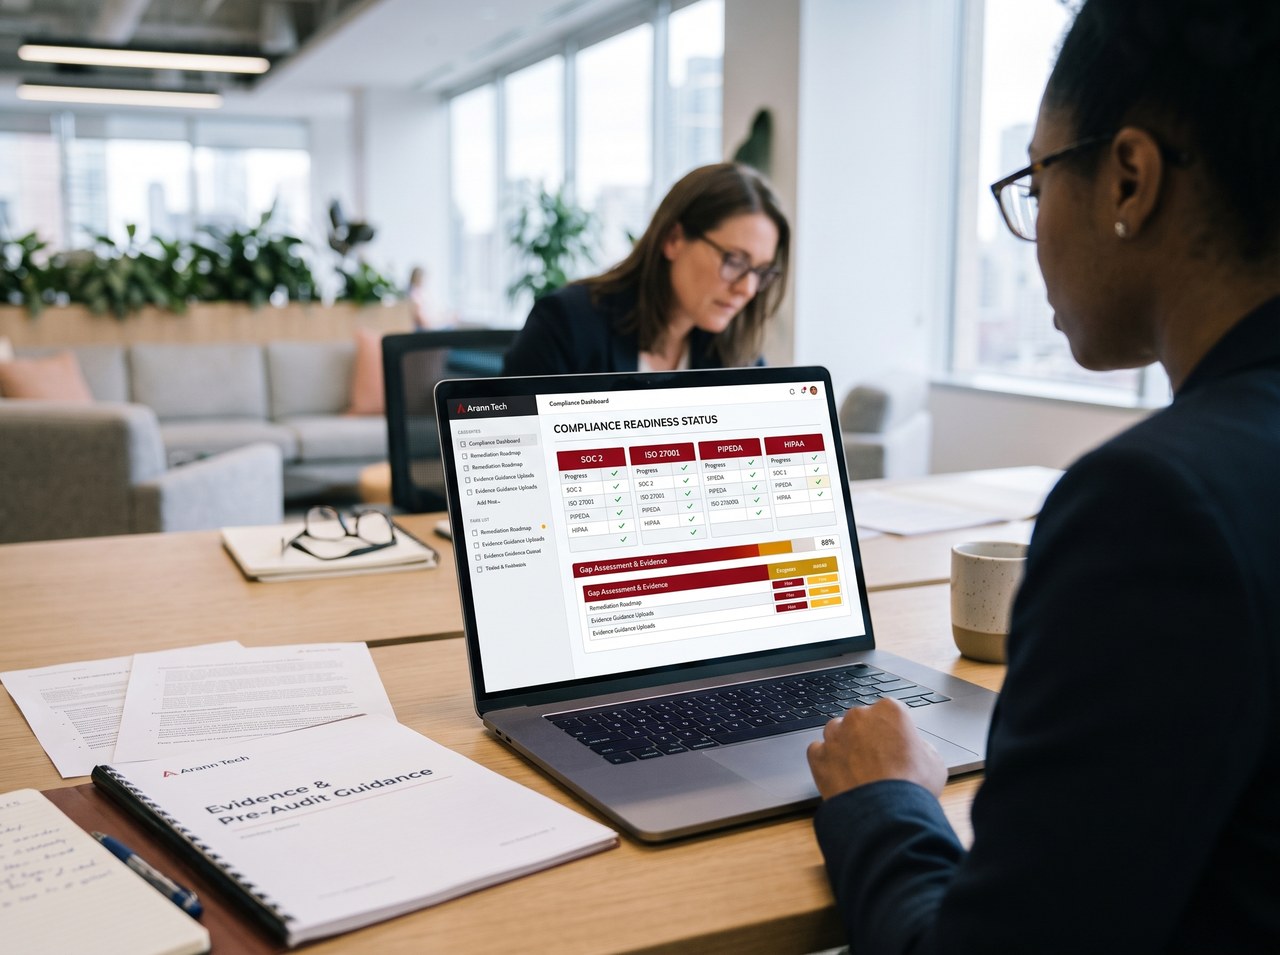
A focused, time-boxed engagement to prepare for a specific audit or certification: SOC 2, ISO 27001, PIPEDA, HIPAA or a client-mandated assessment. Includes a gap assessment, remediation roadmap, evidence guidance and pre-audit review.
Comprehensive benchmarking against framework controls.
Prioritized tasks to eliminate control shortfalls.
Exact documentation and logs required by auditors.
Mock audit walkthrough to ensure complete readiness.
Configured for your team's size and compliance milestones.
| Option | Format | Typical fit |
|---|---|---|
| Risk Assessment / Threat Model | Fixed fee, project-based | New system, migration, pre-audit |
| Compliance Readiness | Fixed fee, 8 to 16 weeks | SOC 2, ISO 27001, HIPAA, PIPEDA |
| Security Leadership Retainer | Monthly, defined scope | Ongoing leadership and risk management |
| Vendor Risk Program | Per-vendor or program | Procurement and renewals |